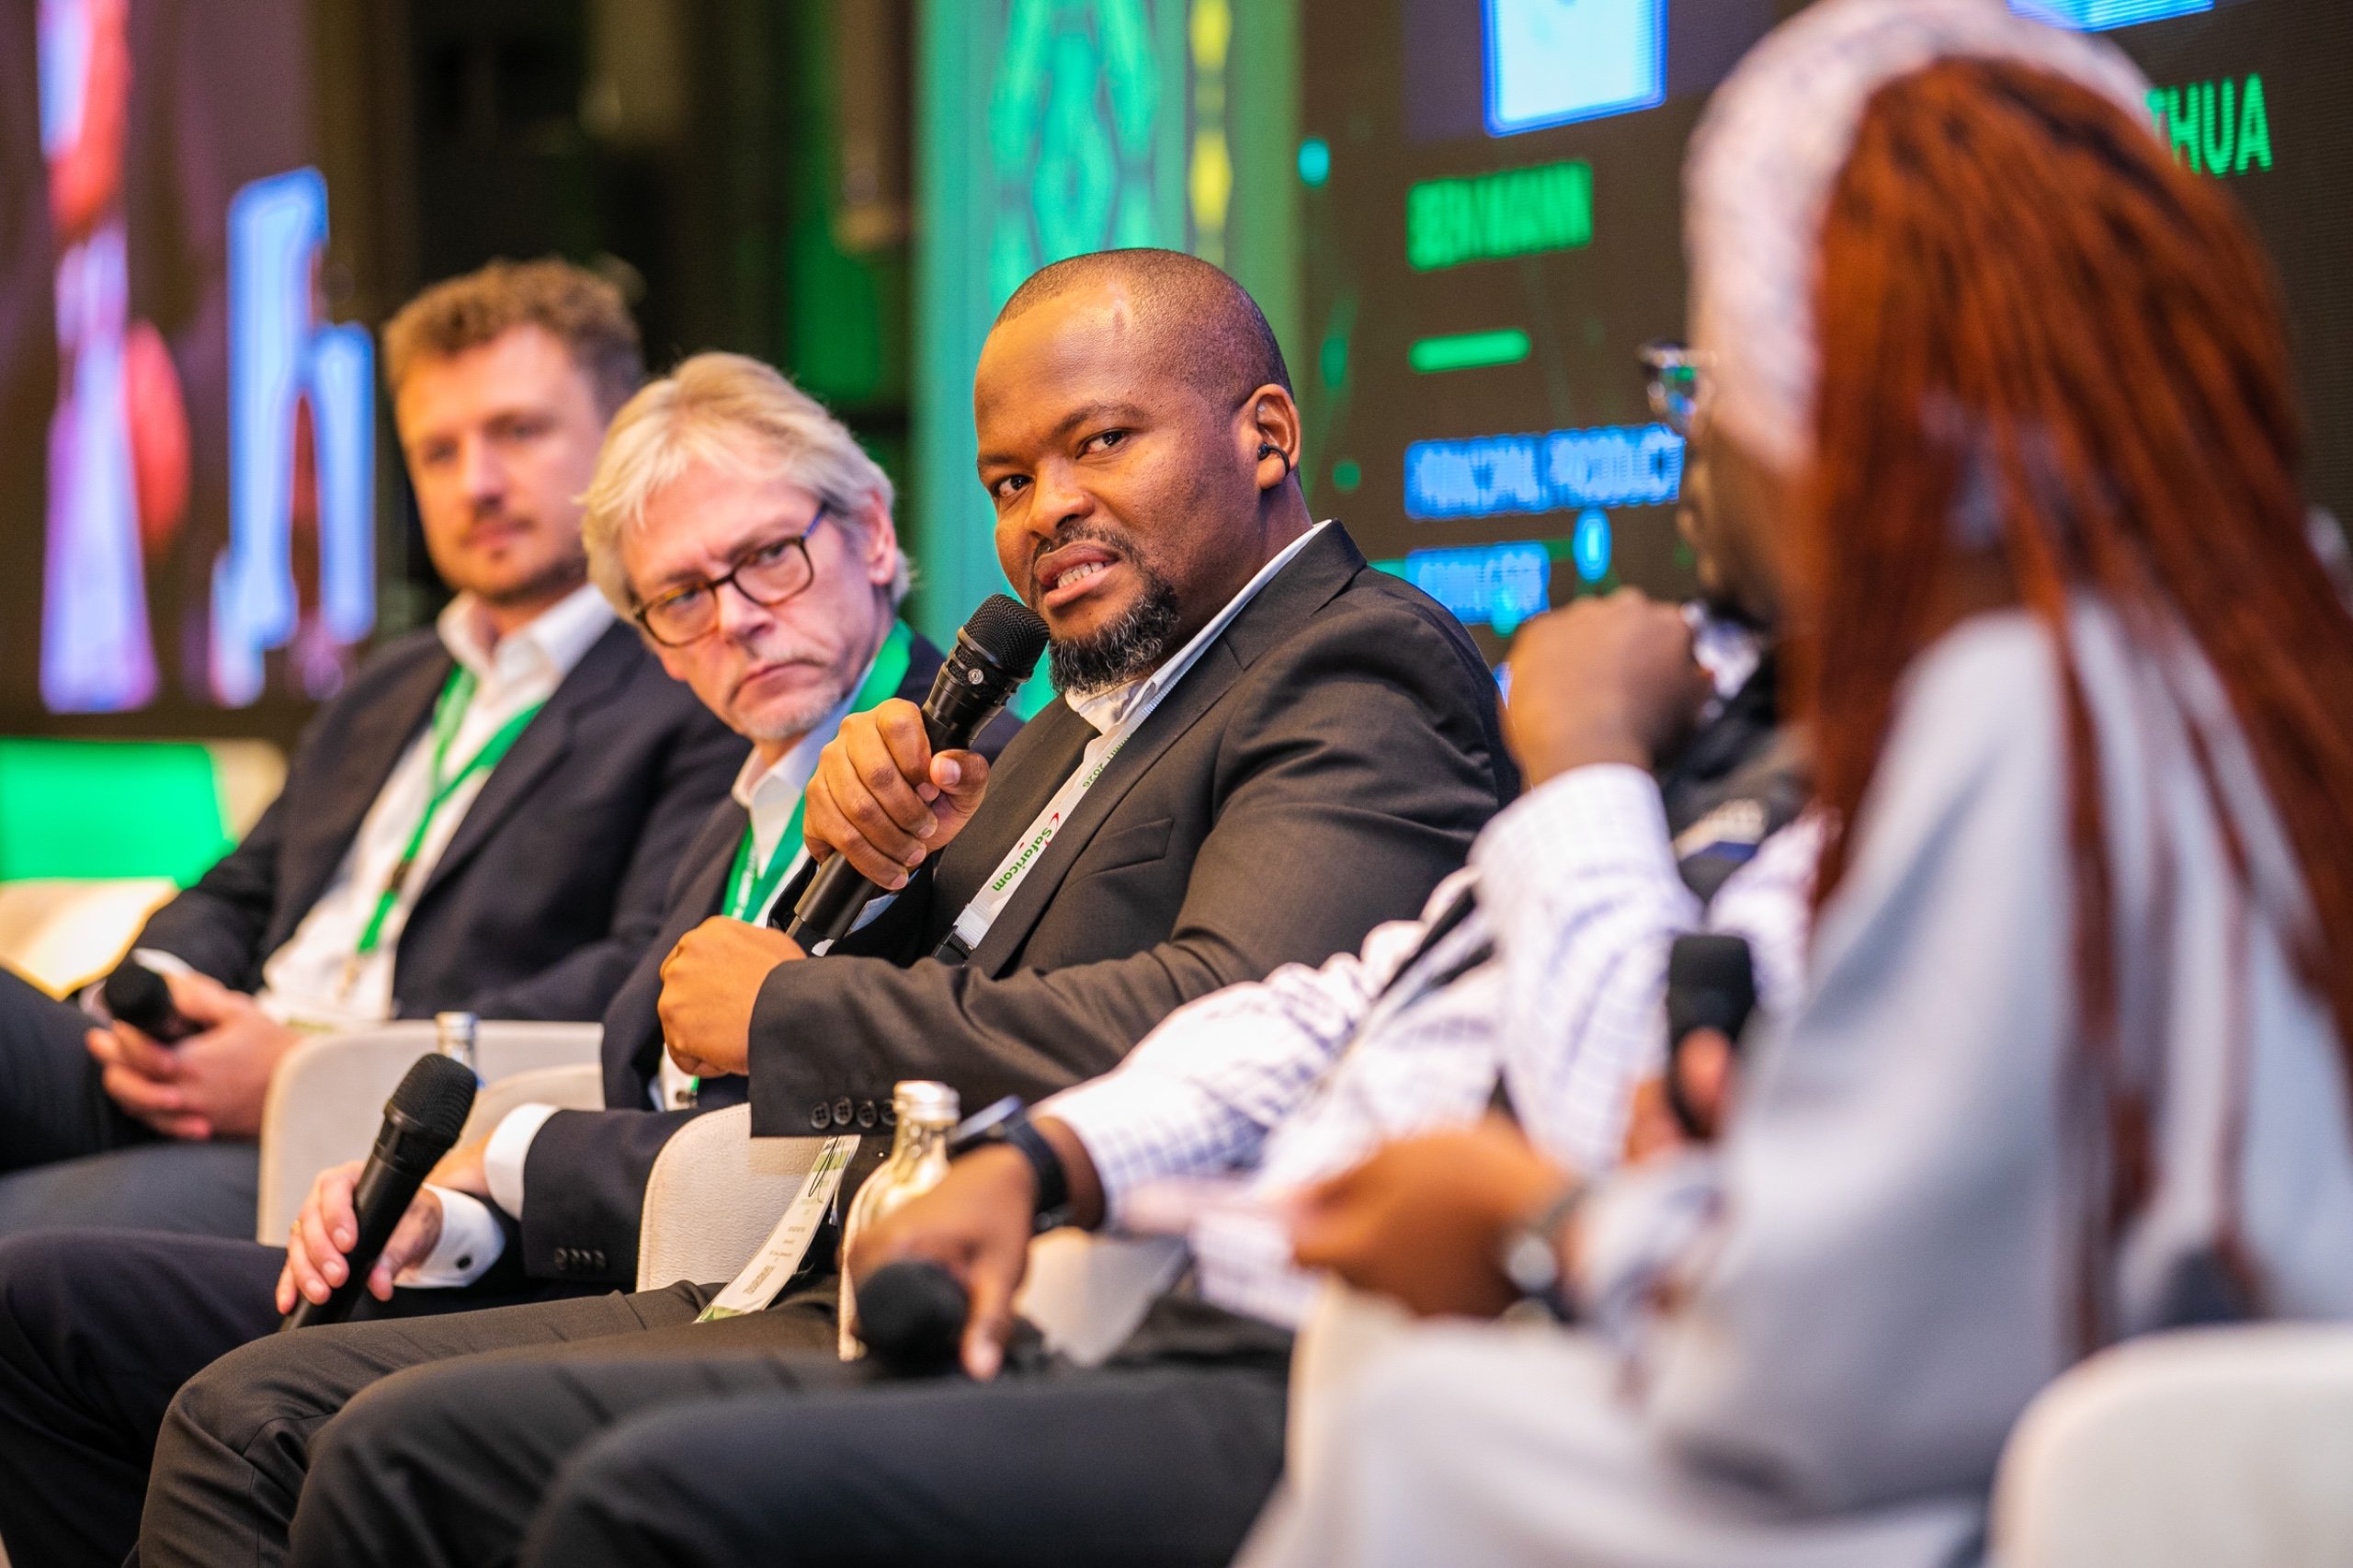
Panelists at the Safaricom Cybersecurity Summit 2026 in Nairobi highlighted that AI‑generated audio and video now allow fraudsters to mimic familiar voices and faces, undermining the long‑standing reliance on personal recognition in business communications.
The core concern expressed was that as synthetic media tools become more accessible, organisations must move beyond visual or auditory cues and embed verification steps that confirm both identity and authority.
Deepfakes can be created using voice‑cloning software that reproduces speech patterns and video‑generation tools that fabricate realistic visual evidence, though not every suspicious clip is necessarily AI‑generated.
For businesses, the greatest risk lies in impersonation attempts that arrive through familiar channels, such as a phone call appearing to come from an executive, and request urgent transfers, supplier‑bank‑detail changes, or confidential data releases.
Payment processes are especially vulnerable because a single fraudulent instruction can cause direct financial loss, especially when attackers create urgency and ask staff to bypass normal approval steps.
The summit recommended that high‑risk transactions be verified through a separate, pre‑established channel—such as calling a known number rather than the one supplied in the request—and that dual‑approval limits be enforced where appropriate.
Technical controls like multifactor authentication, restricted account permissions, transaction alerts and secure account‑recovery processes can limit the impact of a successful impersonation attempt.
Employees are urged to pause when a request feels unusually urgent, asks them to break established procedures, or involves sensitive information, and to verify the request independently before proceeding.
Training programmes should incorporate realistic deep‑fake scenarios so staff can practice verification steps rather than relying on generic warnings.


Comments