Businesses should start by mapping what an AI system does with information, who can access that data and how the organisation will remain accountable for its use.
Common triggers include employees uploading customer records to external AI services, vendors adding AI features to existing software, or automated tools influencing decisions about customers or staff.
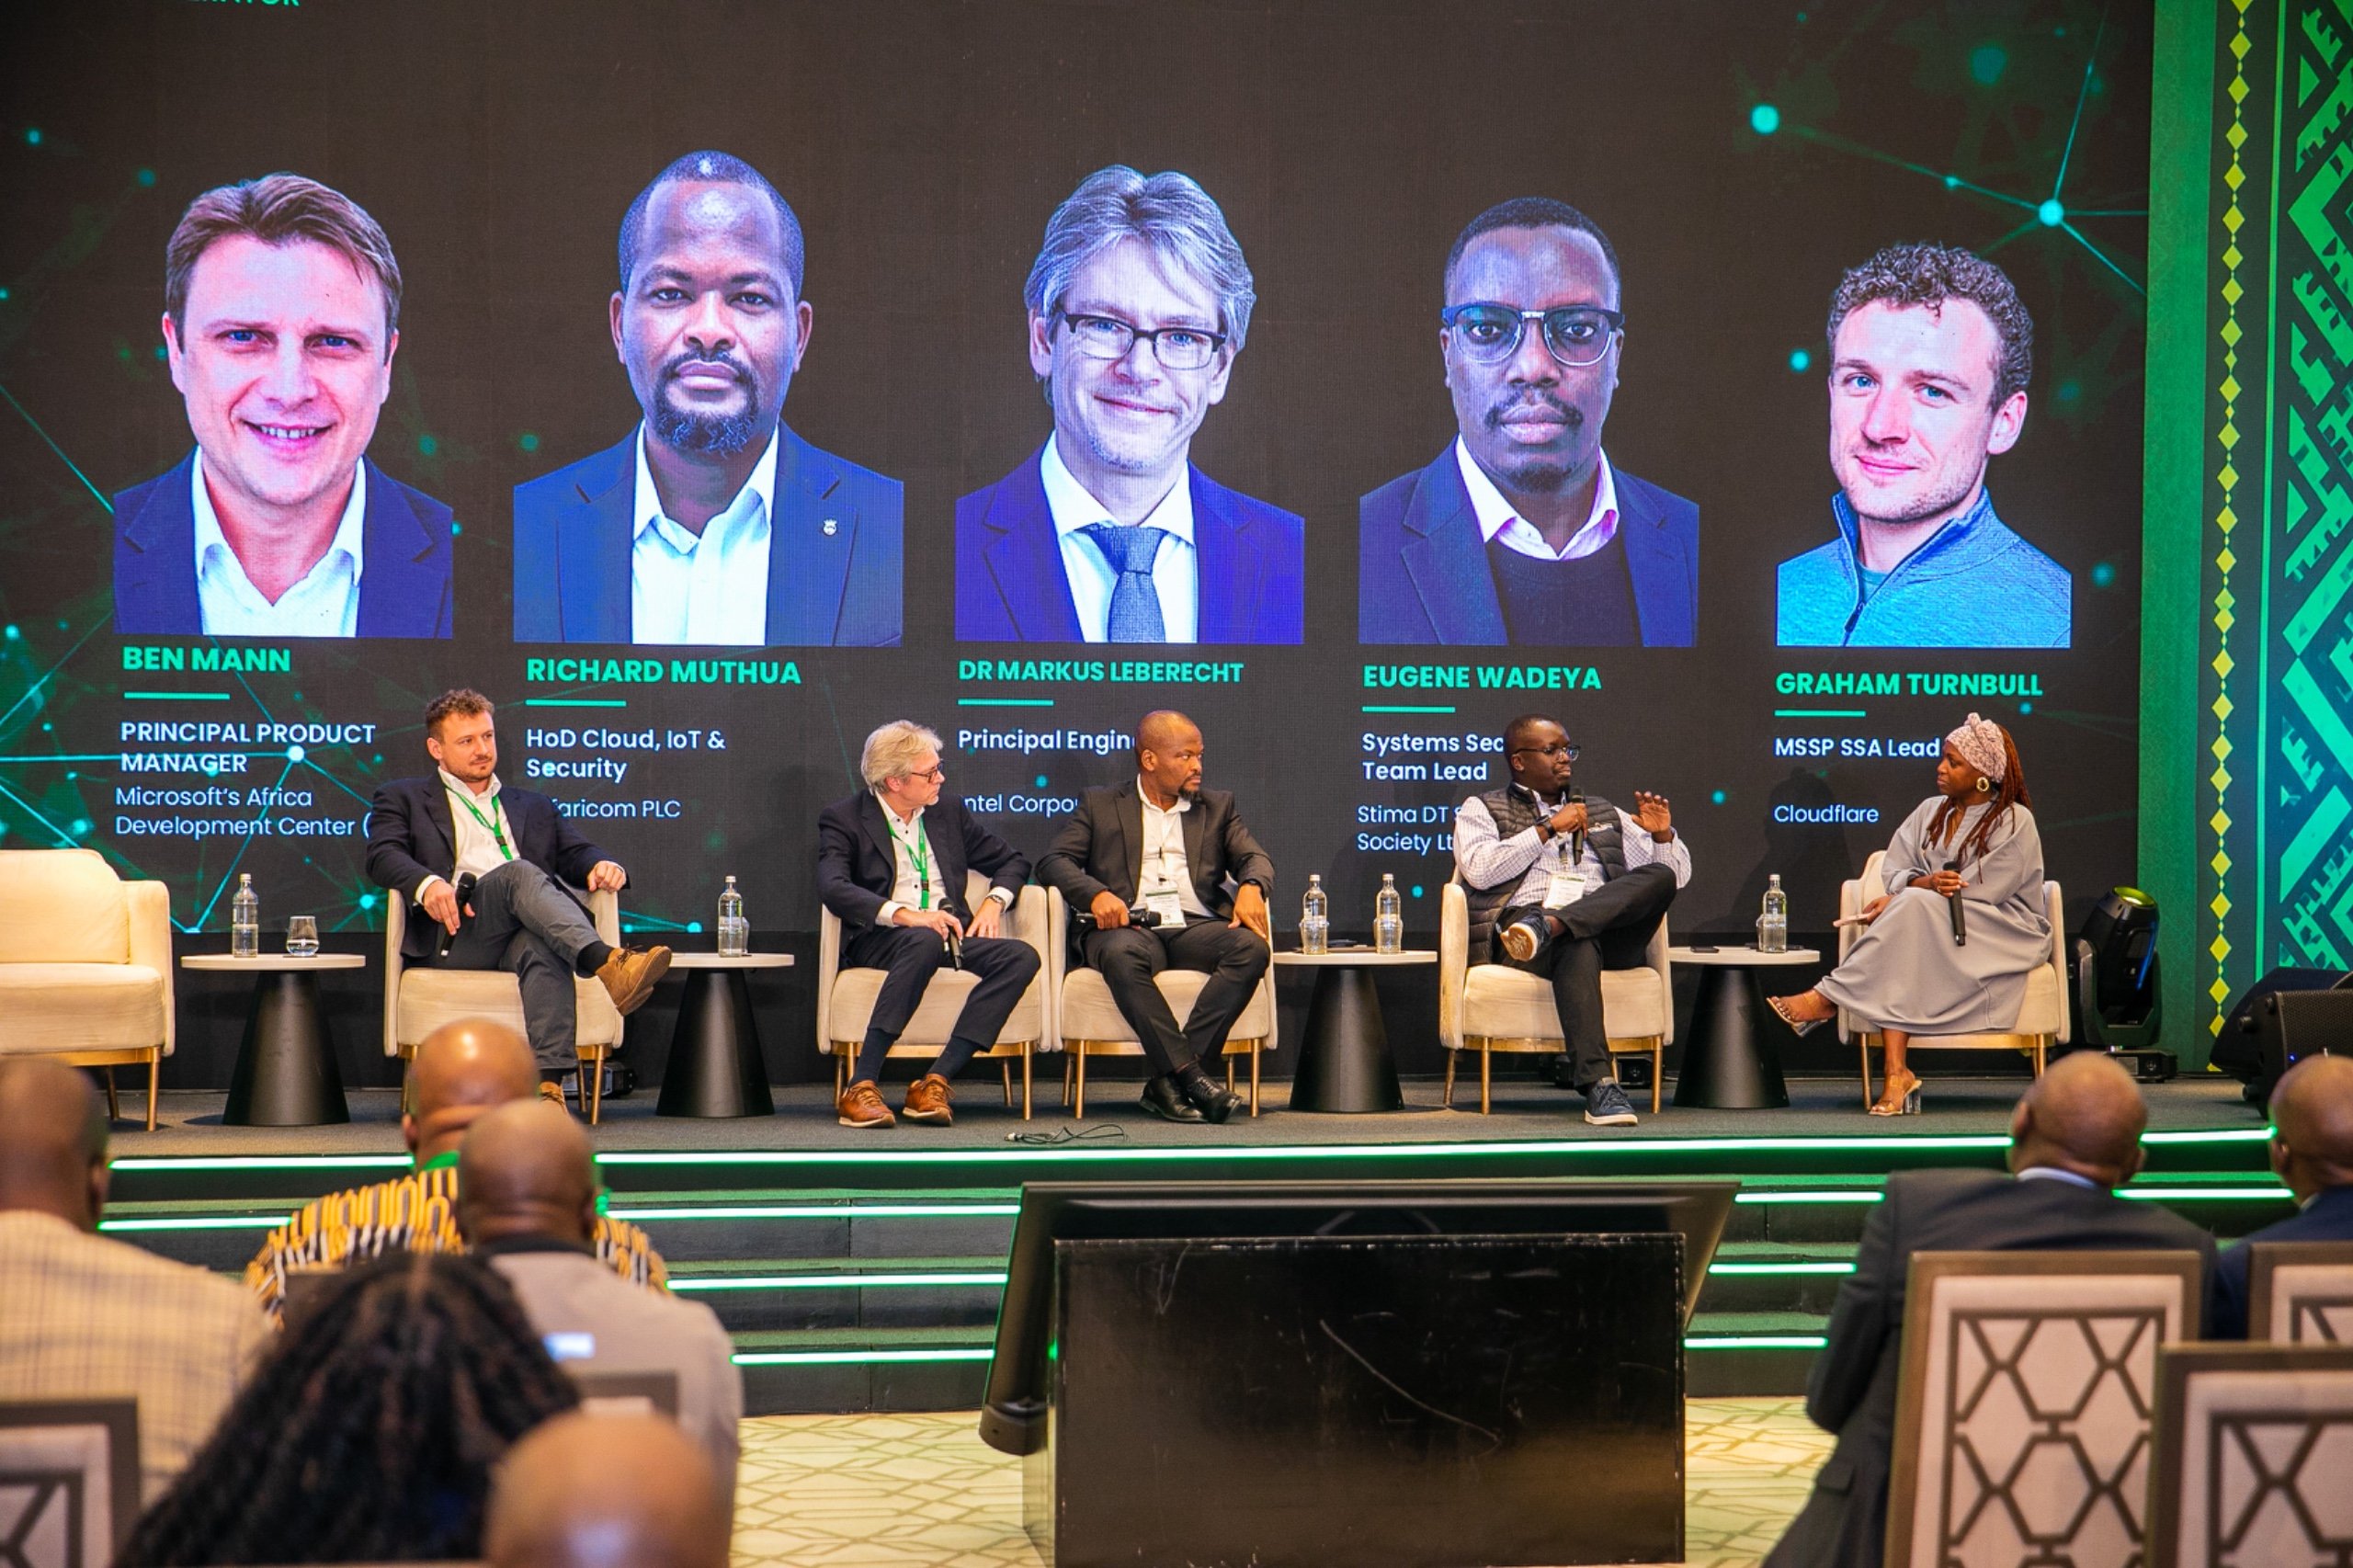
Panelists at the Safaricom Cybersecurity Summit 2026 highlighted the need to classify data, locate processing, and identify the applicable legal regime before deploying AI.
Kenya’s Data Protection Act, 2019, remains the core framework for personal data, requiring lawful processing, safeguards for cross‑border transfers and clear accountability.
The EU GDPR may affect some organisations, but Kenyan companies should not assume it automatically applies nor that using an overseas service removes their responsibilities under Kenyan law.
A practical review begins with an inventory of AI tools and the business purposes they serve, followed by identification of data categories, access points, and retention arrangements.
High‑impact uses may require stronger oversight, more detailed risk assessment and clear routes for people to challenge decisions.
Human review must be meaningful, giving reviewers sufficient information and authority to question AI outputs rather than merely rubber‑stamping recommendations.
Governance structures should assign AI oversight across technology, security, legal and business teams, document approved uses, restrict access by role and provide staff training on data handling and incident reporting.
Periodic reassessments are essential because vendor feature changes, new data categories or altered business purposes can shift risk profiles.
Embedding clear data‑governance, proportionate security controls and accountable human oversight enables Kenyan firms to reap AI benefits while meeting legal obligations.


Comments